One workspace. The whole investigation.
SOCPilots Platform
From alert
to understanding.
Alerts, entities, cases and response. Bring the investigation together without leaving your existing SIEM behind.
The console
Real application views with synthetic demonstration data. No customer alerts, cases or accounts.
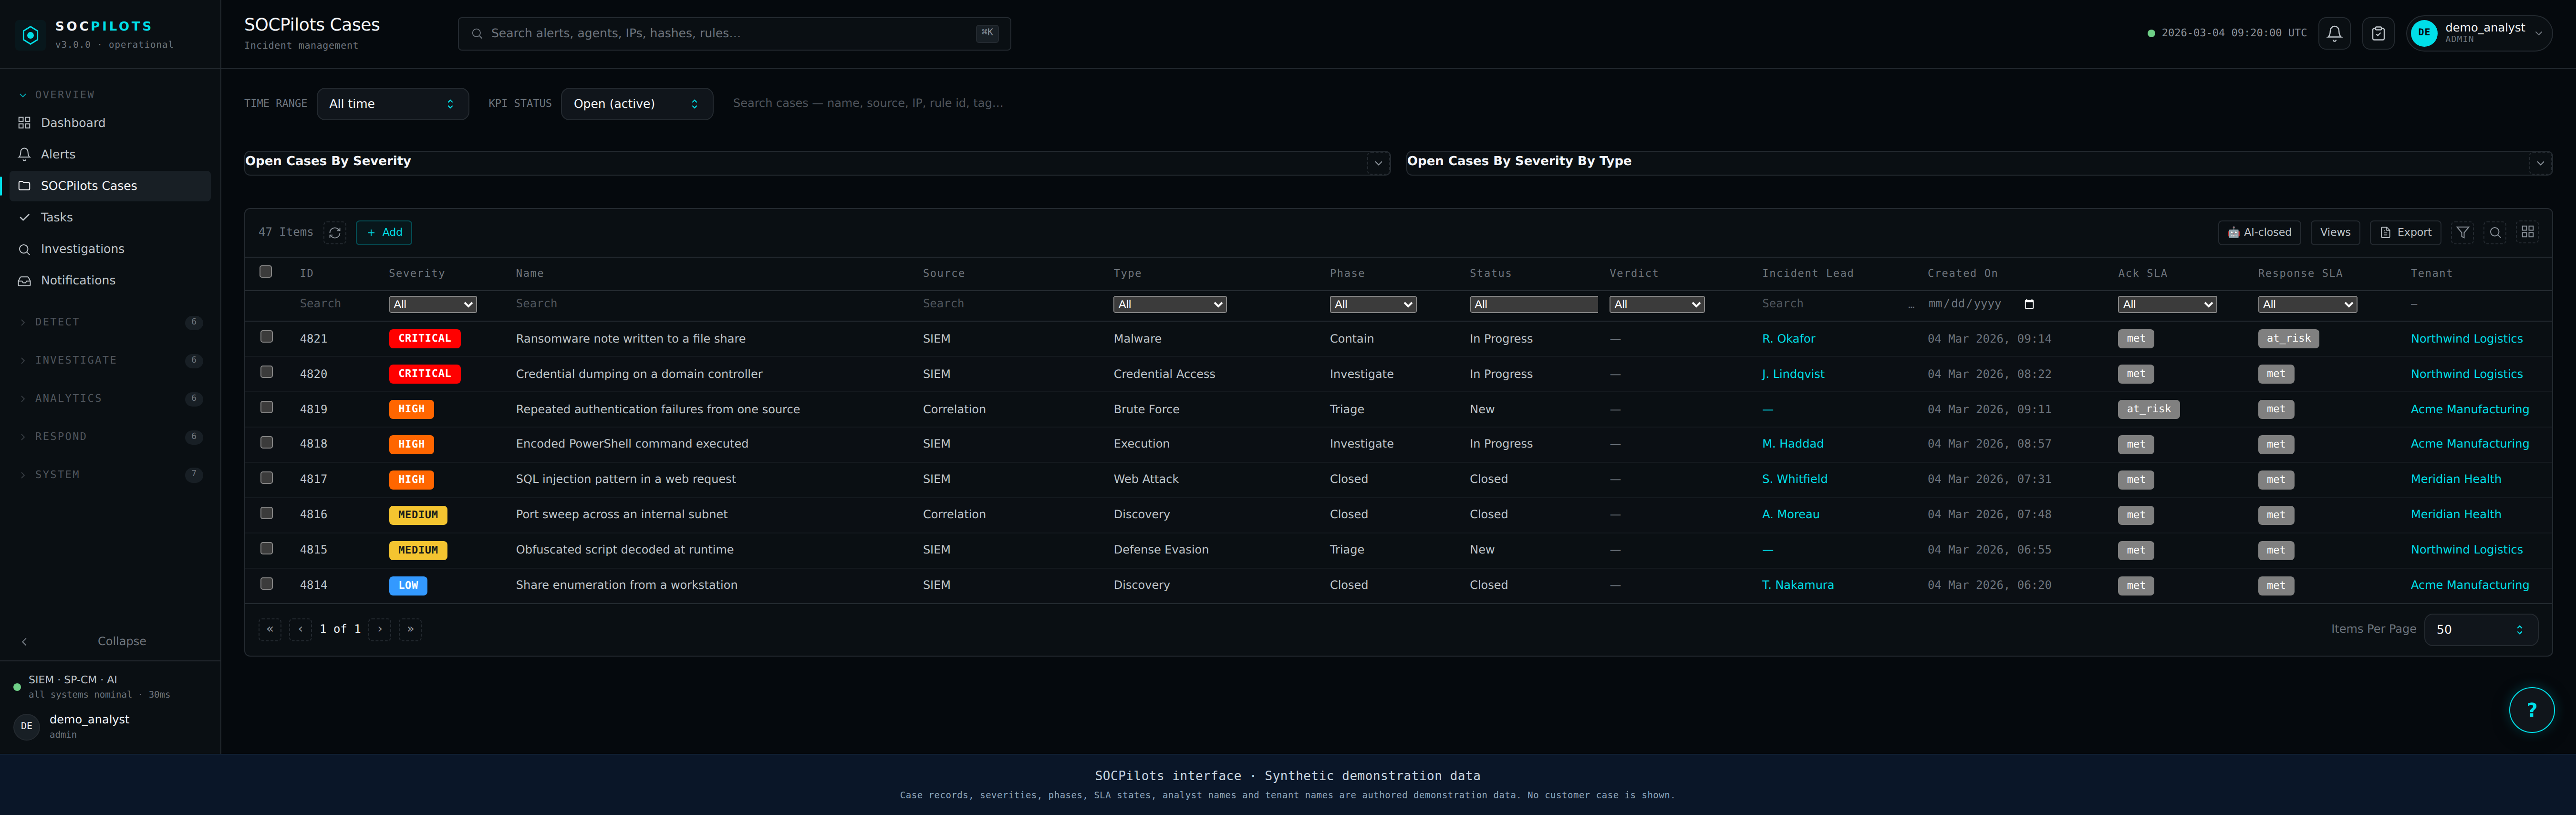
Open the full-resolution image to read the detail — 5400 × 1708 pixels.
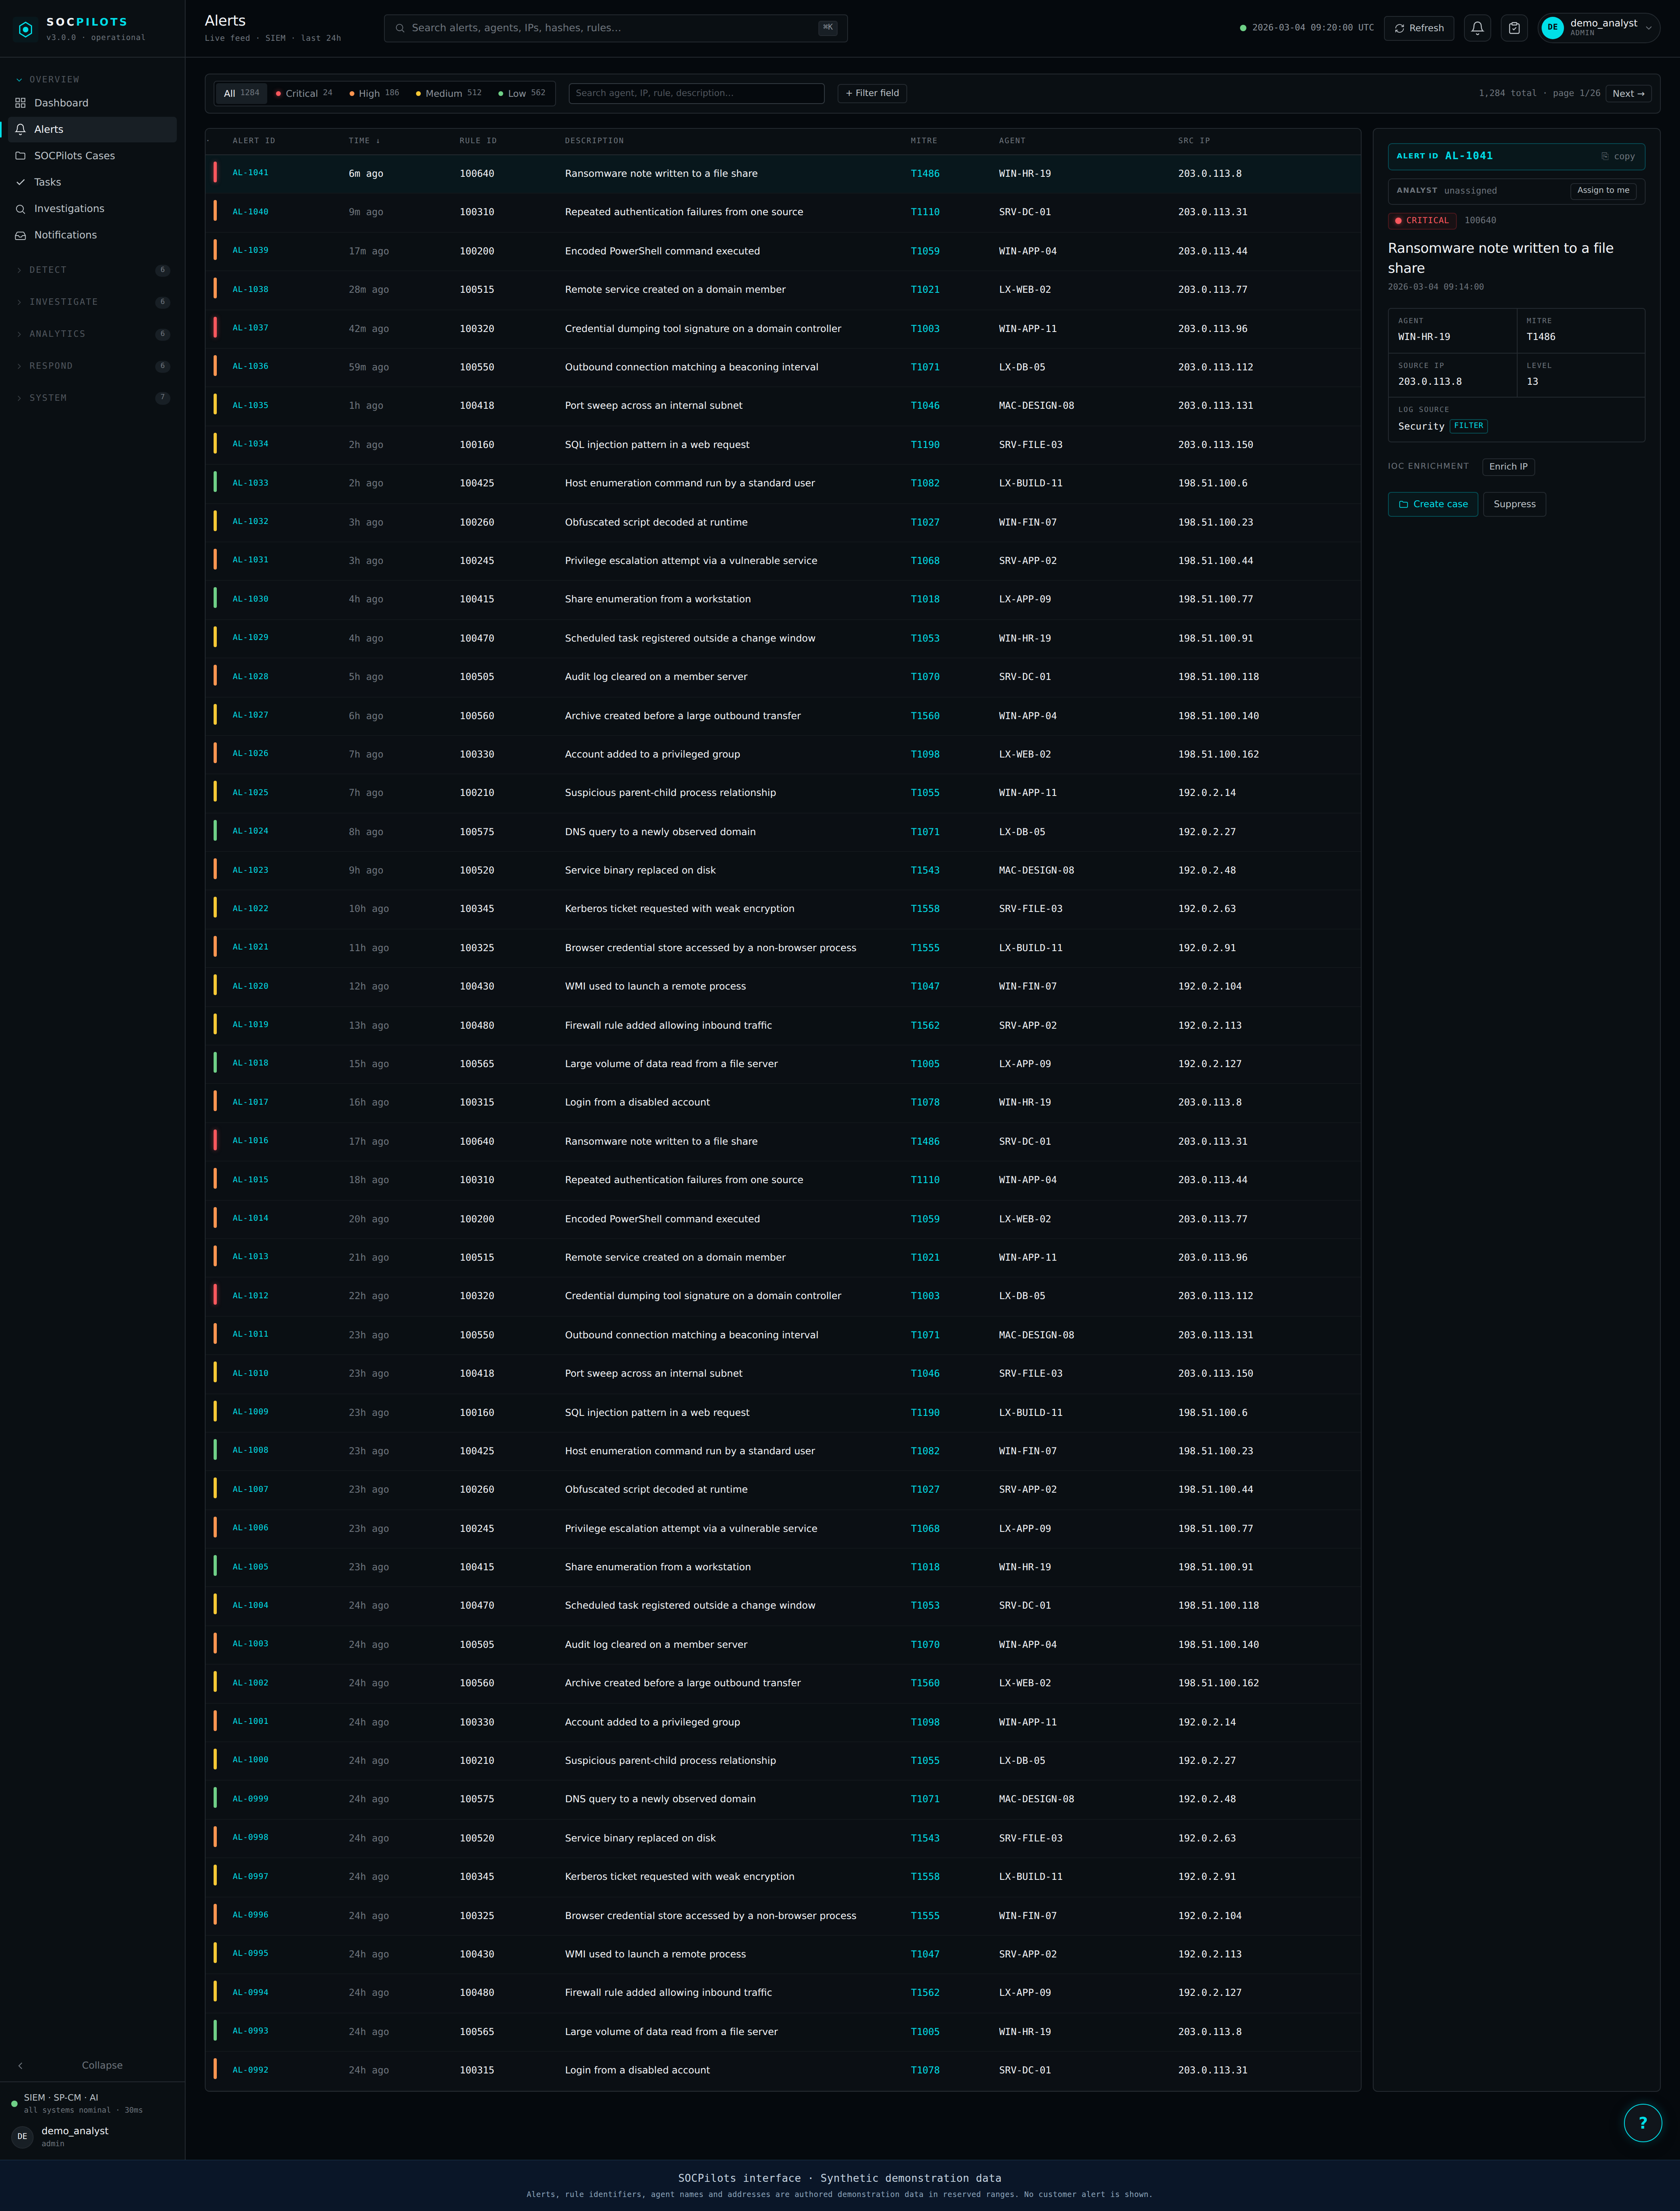
Open the full-resolution image to read the detail — 4200 × 5528 pixels.
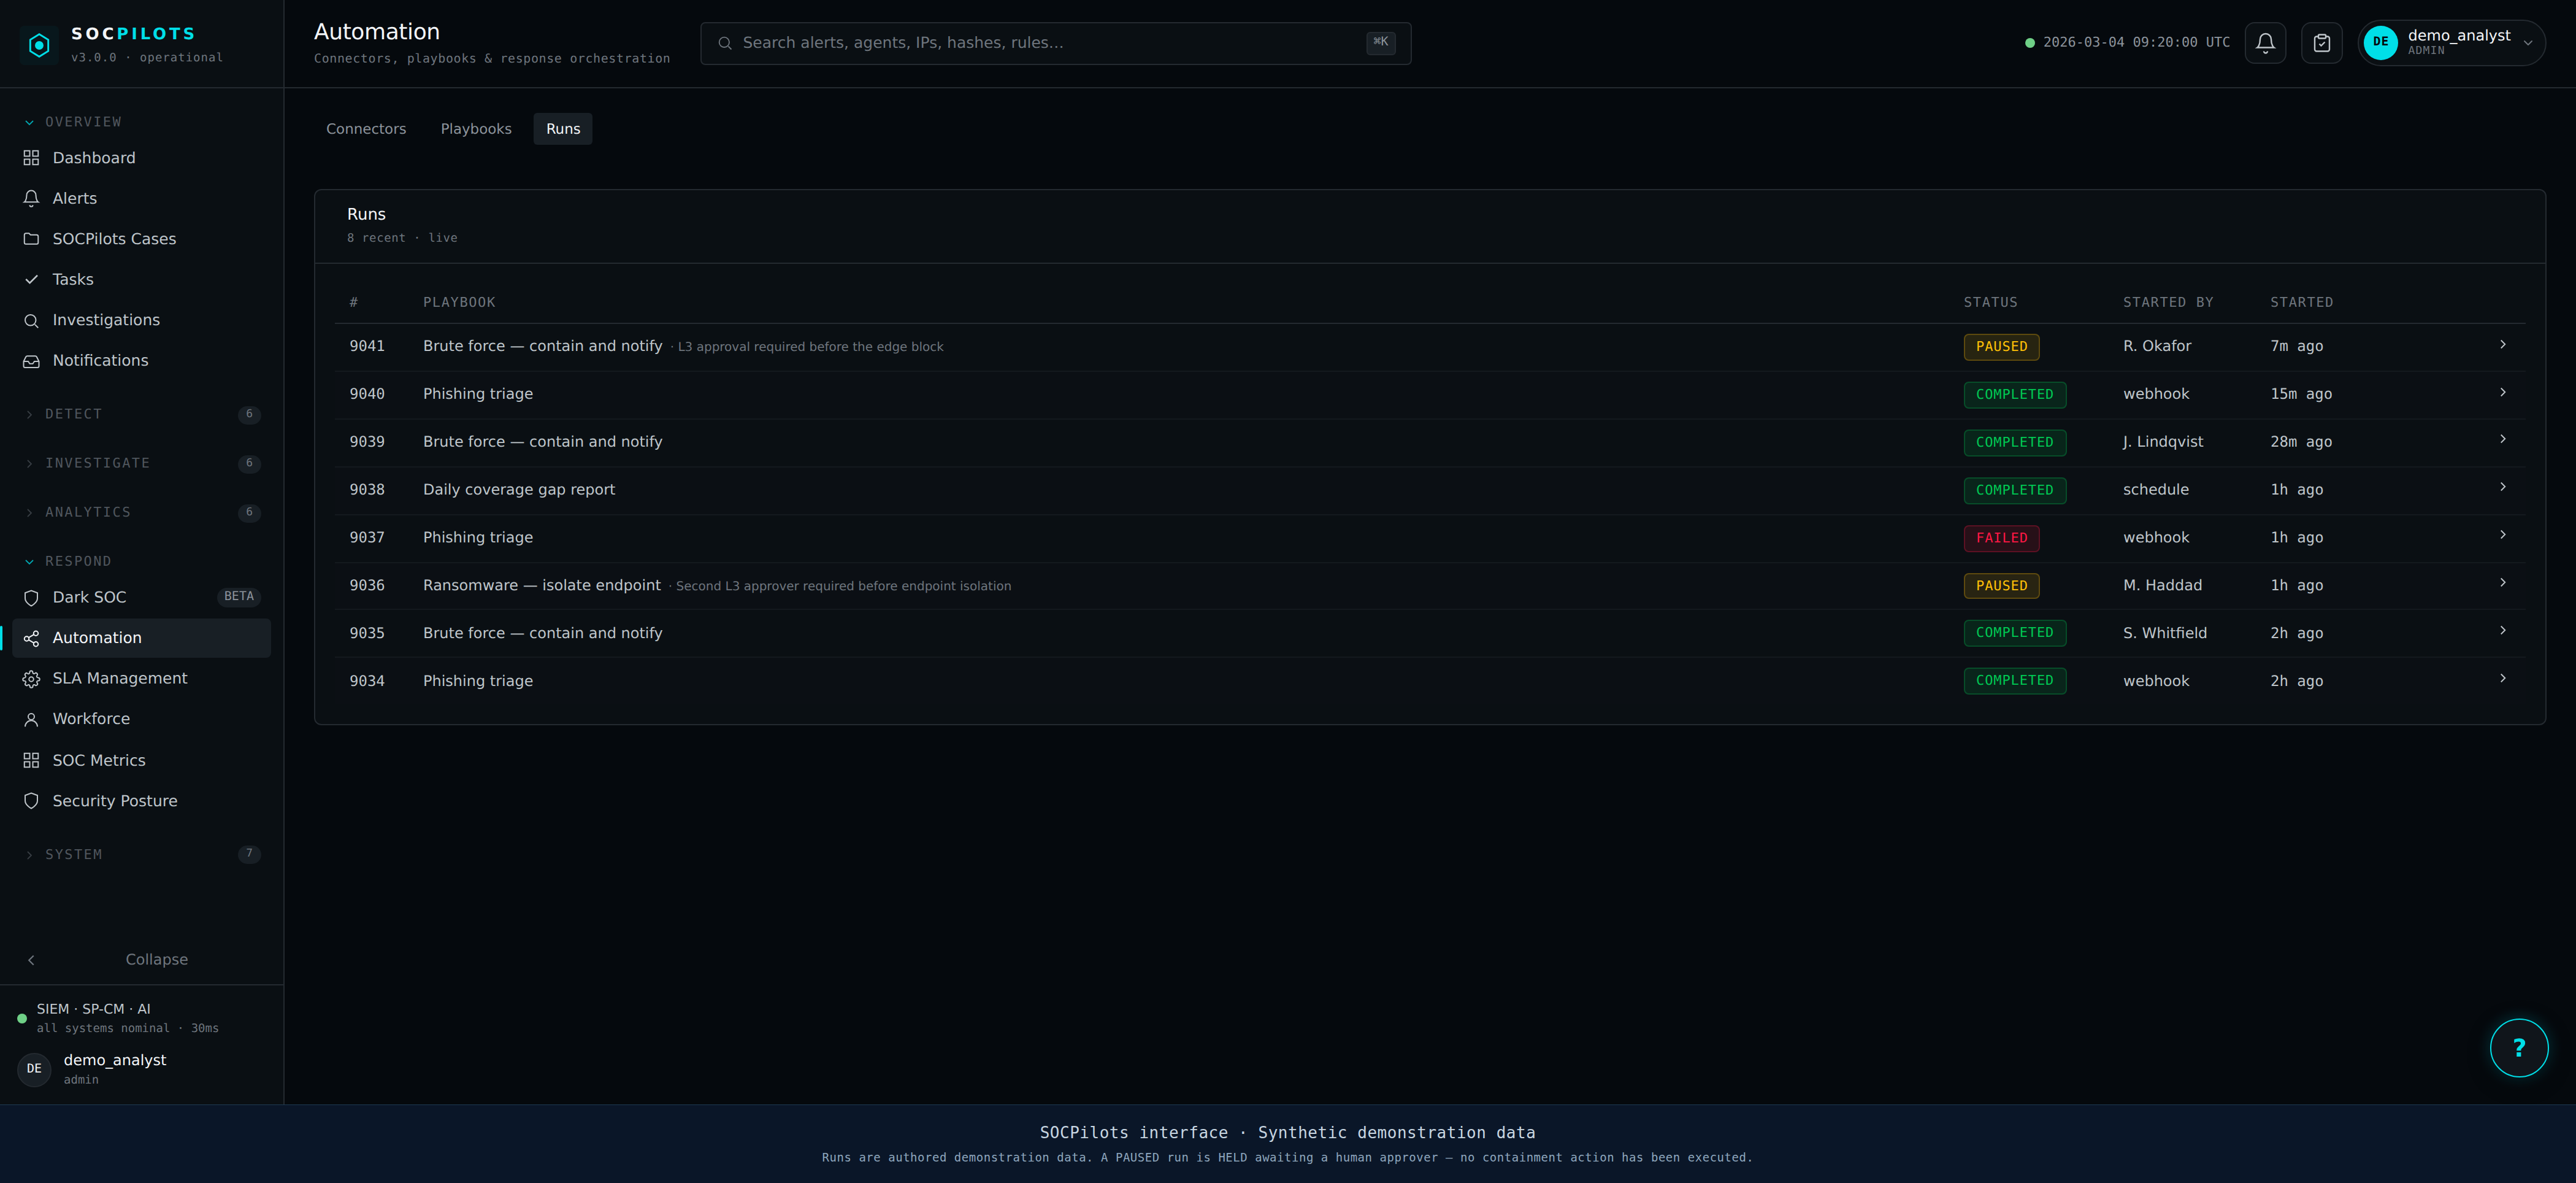
Open the full-resolution image to read the detail — 4200 × 1928 pixels.
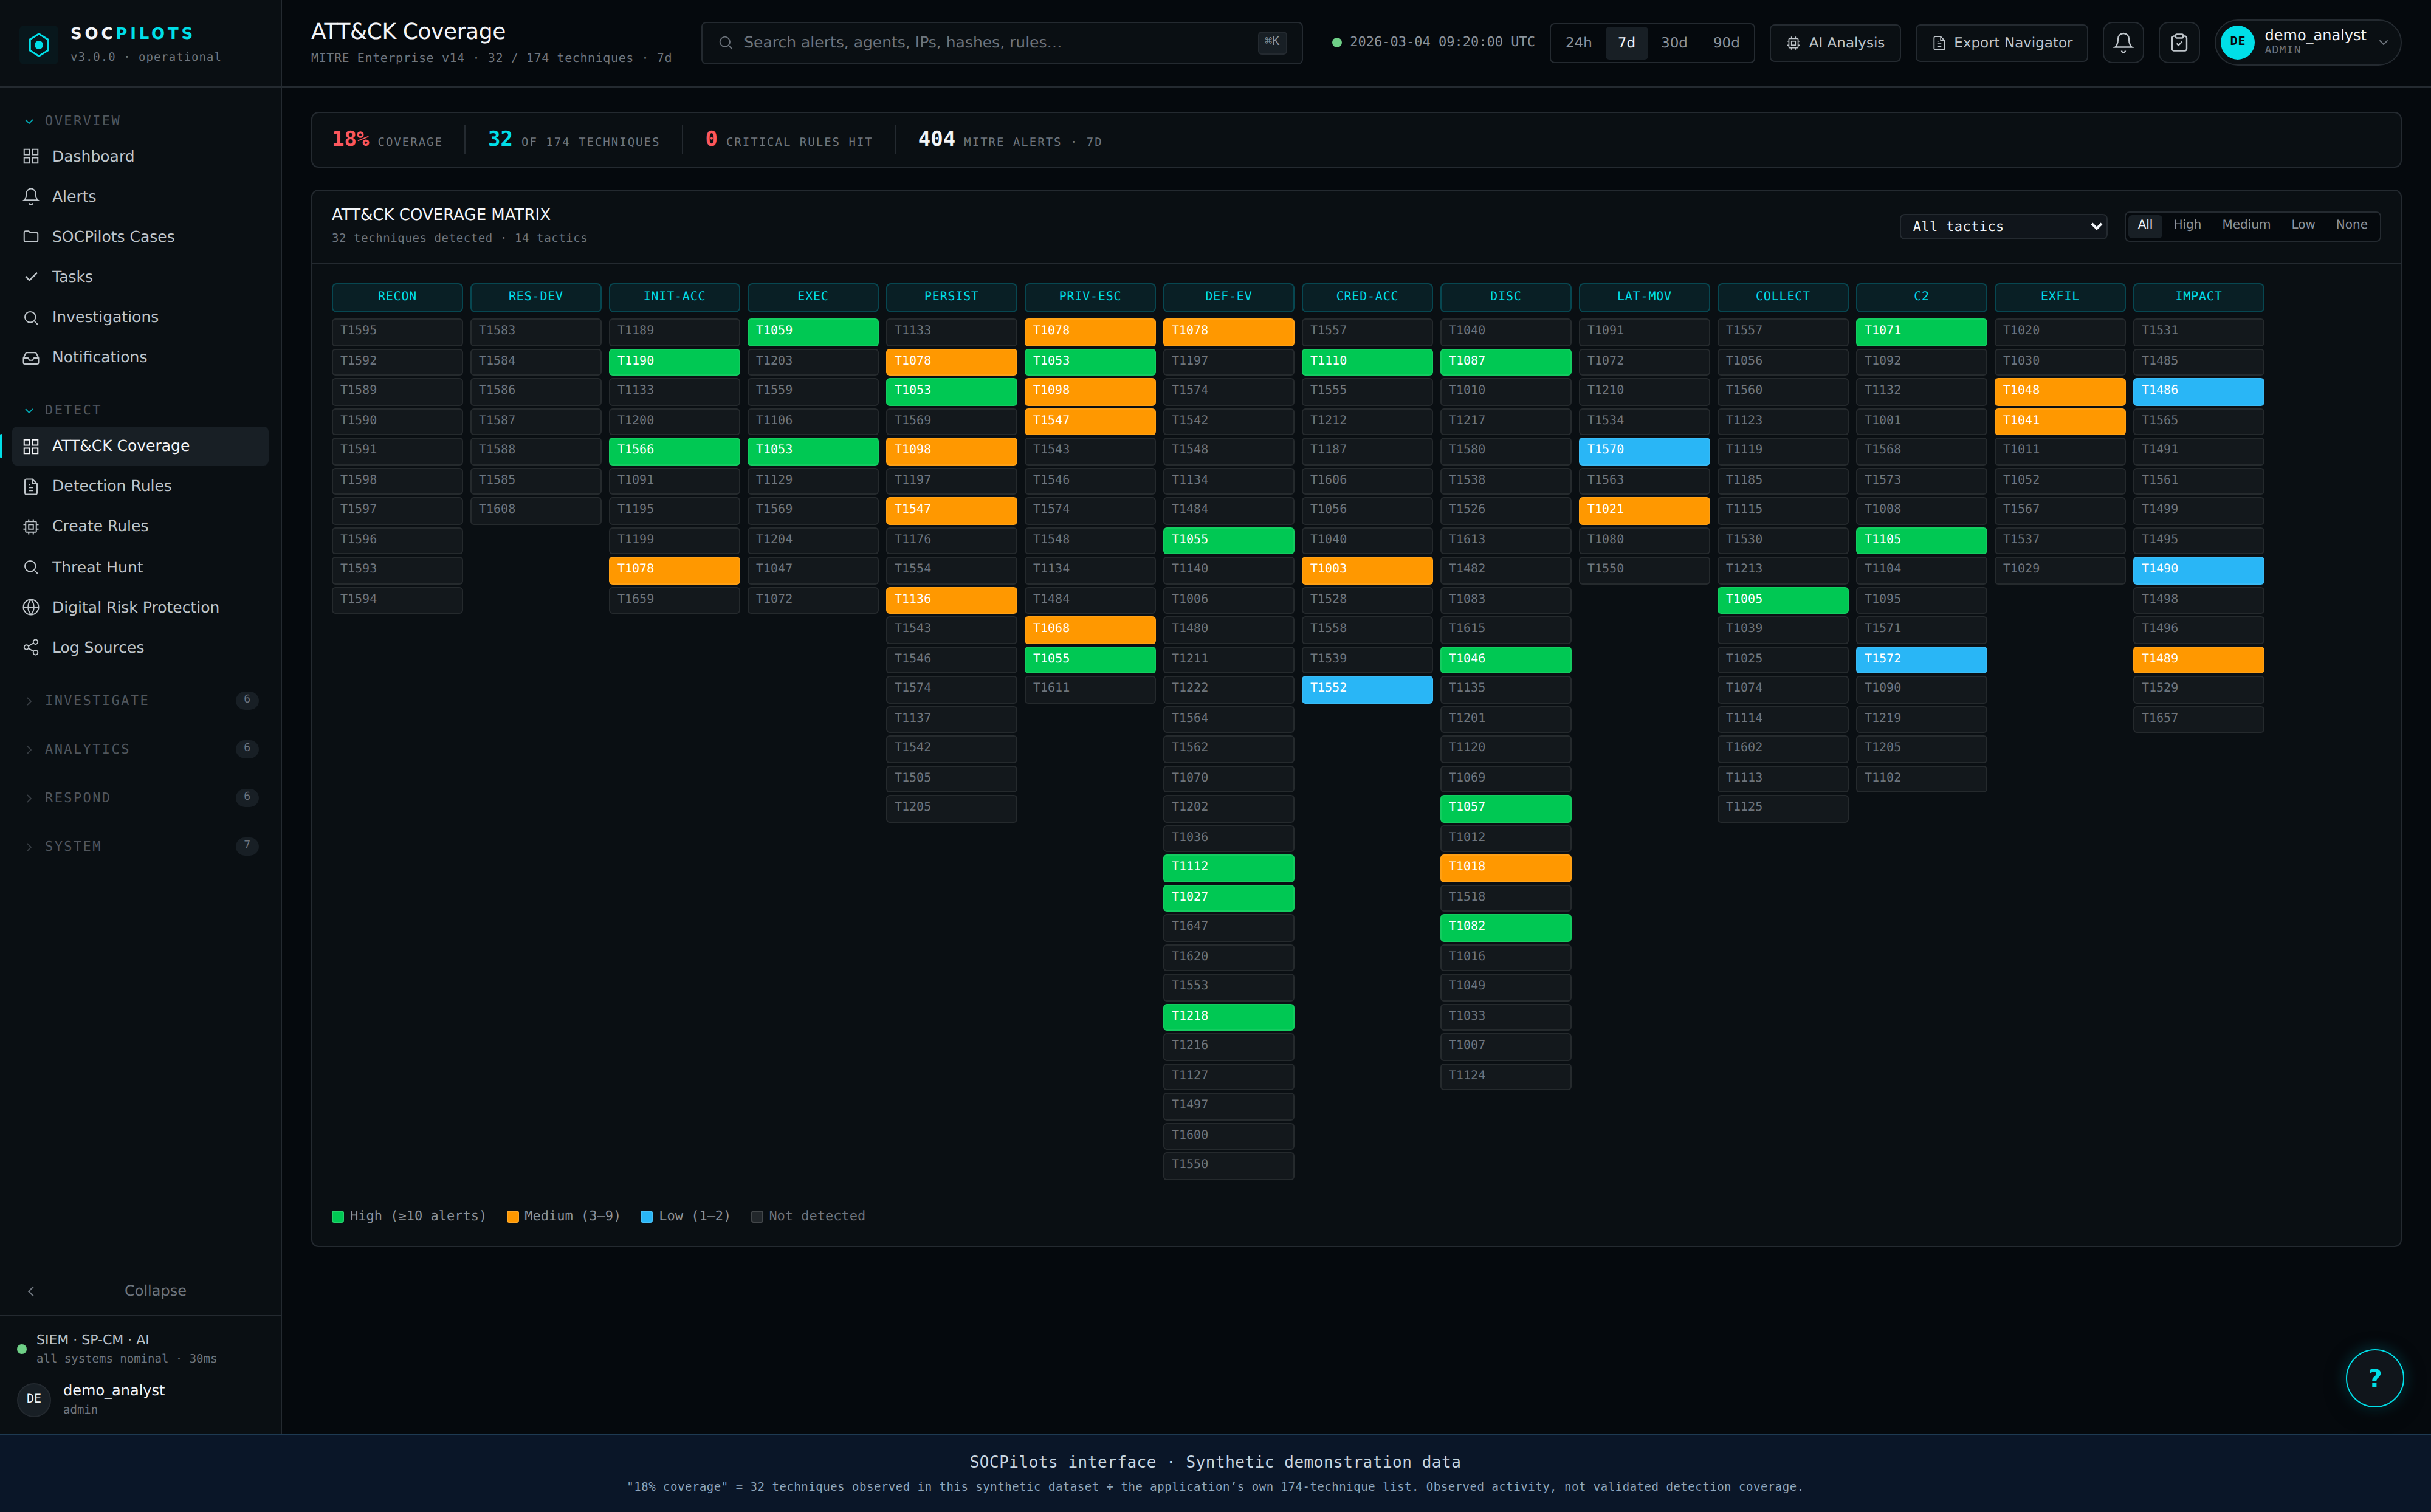
Open the full-resolution image to read the detail — 4000 × 2488 pixels.
SOCPilots is a desktop console. These are wide screenshots: on a narrow screen open the full-resolution image to read them.
From signal to judgement
From incoming signal to a recorded outcome, with evidence and review along the way.
01Ingest
Connect your SIEM and normalize incoming alerts while retaining their source context.
Result: searchable, comparable events.
02Correlate
Identify repeated and related signals using configured grouping rules. Correlation links evidence; it is not the same as creating or closing a case.
Result: related alerts grouped for investigation.
03Investigate
Bring available asset context, threat intelligence and entity relationships into the investigation.
Result: evidence an analyst can inspect.
04Decide
Review evidence and risk, record a verdict, and route actions through configured policy and approval requirements.
Result: a documented decision.
05Respond
Run supported connector actions and review execution results. Availability depends on the connected environment.
Result: recorded action outcomes.
SOCPilots in action
Watch an investigation
take shape.
From a suspicious alert to reputation checks, account context and an evidence-backed finding for your team.
Cases that hold the whole story
Investigation is a record, not a chat log. Everything that happened to a case stays attached to it.
Case management, ownership, evidence and service levels
Cases
casesAlerts, evidence, tasks and a timeline in one record. Closure requires a disposition and a closure note.
Tasks and ownership
tasksAssign and track case work. With workforce management enabled, route new cases by shift and available capacity.
Evidence
evidenceKeep documents, exports and screenshots with the investigation. Extract and index text for later searches.
Collaboration
commentsNotify colleagues with account-linked mentions in cases, tasks and war rooms.
Service levels
slaTrack response and resolution against your policy, including configured business hours and breach warnings.
Entity intelligence
A relationship changes
the investigation.
Follow the identity, host, process and destination behind an alert. Inspect the connections before drawing a conclusion.
svc_backup
A service account links the activity across hosts. An unusual relationship is evidence to investigate, not a verdict.
Illustration, not live telemetryThe rest of the console
Coverage, intelligence, assets, vulnerabilities and reporting
ATT&CK coverage
Explore techniques observed in alerts and their associated rules, agents and activity. Export to MITRE Navigator to support detection planning. Observed activity is not validated detection coverage.
Threat intelligence
Indicators are enriched against reputation and pulse feeds, cached so the same address is not looked up forty times an hour, and cross-referenced against a stored indicator feed that raises the score on anything already known bad.
Assets and exposure
Discover what is on the network, track criticality and ownership, and find the hosts your SIEM has no agent on — the blind spots that make coverage numbers look better than they are.
Vulnerabilities
Exposure per asset, tied back to the same inventory the cases use, so a vulnerability on a tier-0 host reads differently from the same vulnerability on a lab machine.
Reporting
Operational reporting for the people running the shift, and executive reporting for the people funding it. Volumes, response times, coverage, and what changed since last month.
Digital risk
Monitoring beyond the perimeter — credential leaks, brand abuse and dark-web mentions — brought into the same case system as everything else.
One console, five points of view
Role decides what a person sees and what they are allowed to do. It is a permission model, not five different products.
Roles and responsibilities
Analyst
l1 · l2Works the queue: triage, enrich, document, respond. Sees their own tenant and their own assignments first.
Senior analyst
l3Owns escalations, approves containment requested by others, and authors detection content.
SOC manager
reportingWatches queue health, response times, shift coverage and service levels, and reassigns work when a queue tips over.
Administrator
adminConfigures connections, users, policies, automation and workspaces, with administrative changes recorded in the audit trail.
Executive and client
read onlyPosture, risk and outcomes without the operational detail — and, for a managed customer, a view shaped by the role-based permissions you grant them.
See it against your own backend
A demo on your SIEM tells you more than a demo on ours.